Matrix Scroll
Open protocol for signed machine-action authorization records. The Python SDK on PyPI verifies envelopes offline. No account is required for local signing or verification.
/schemas/*, and the PyPI
package remain the public trust surface. Details:
OFFLINE-SHUTDOWN.md.
Gold standard
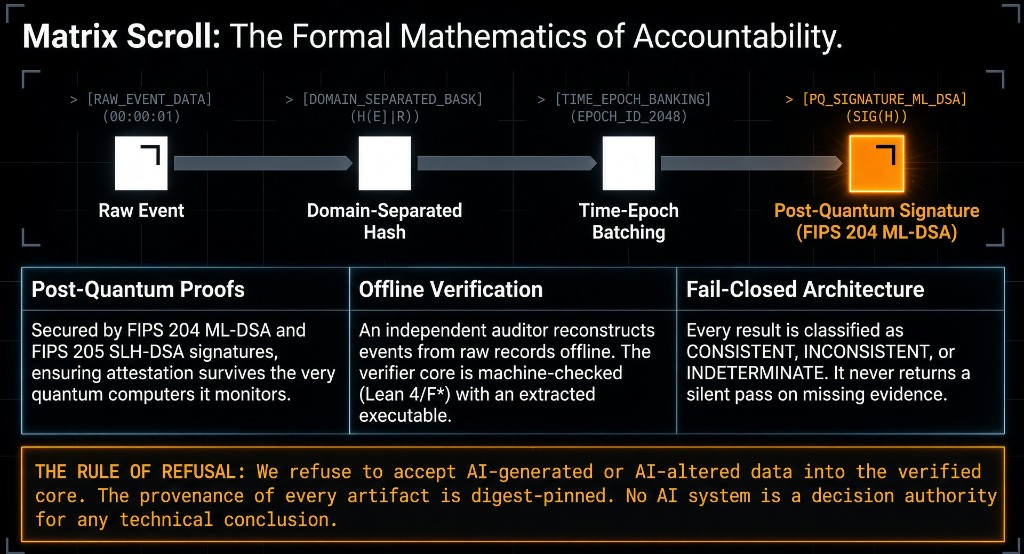
Shipping: raw event to domain-separated hash (matrixscroll.ledger) to
time-epoch checkpoints to Ed25519 with optional FIPS 204 ML-DSA overlay. Offline
verification. Fail-closed verdicts: CONSISTENT, INCONSISTENT, or INDETERMINATE.
Bar: ML-DSA-only primary as default, and a Lean 4 / F* extracted verifier.
Install
pip install "matrixscroll==0.10.0"
Release 0.10.0 ships a hash-linked ledger with signed epoch checkpoints,
device-agnostic custody (implement IdentityProvider; default is the
file-backed emulated provider), optional Cat-5 sealed evidence packs
(X25519 + ML-KEM-1024, Ed25519 + ML-DSA-87), and opt-in primary ML-DSA-87
via MATRIXSCROLL_PRIMARY_ALG. Install matrixscroll[pqc] for the
post-quantum path.
Verify offline
Verification does not contact this domain. Schema $id values name
matrixscroll.com; the SDK loads schemas from the installed package.
matrixscroll verify path/to/signed.json
matrixscroll envelope-verify "$(git rev-parse HEAD)"
matrixscroll envelope-verify-range --source local HEAD~5..HEAD
matrixscroll ledger verify --bundle path/to/ledger-bundle.json
Documentation and specification
Security
Report vulnerabilities privately. Do not file public GitHub issues for security bugs.
- GitHub Security Advisory (preferred)
- Email security@matrixscroll.com
- SECURITY.md
Commercial
The verifier and protocol are Apache-2.0. SSX360 supplies hosted Scroll Gate and commercial control-plane options separately: ssx360.com/contact.